SAP NetWeaver EP CVE-2025-42884: JNDI injection added to KEV
Unauthenticated JNDI injection in SAP NetWeaver Enterprise Portal 7.50. CVE-2025-42884, SAP Note 3660969, NVD/CISA status, and patching priority.
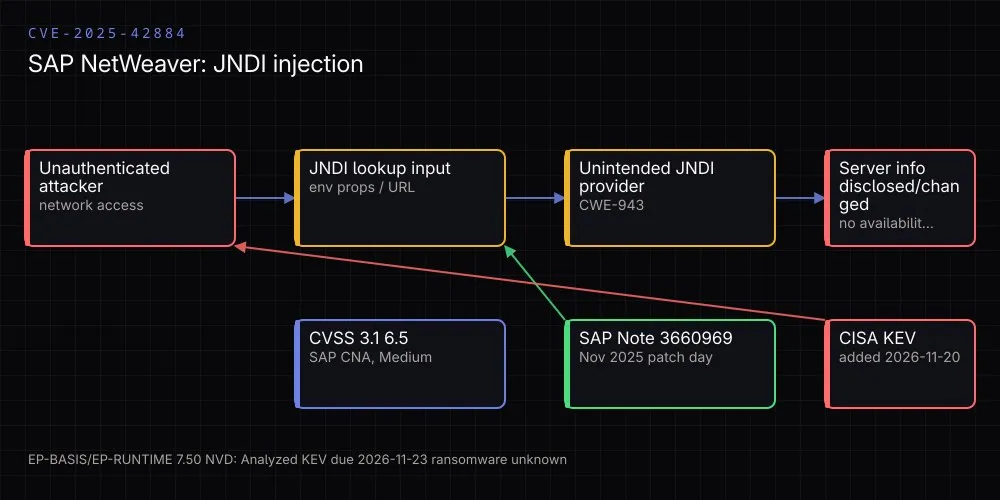
On November 20, 2026, CISA added CVE-2025-42884 to the Known Exploited Vulnerabilities catalog. The flaw allows unauthenticated JNDI injection in SAP NetWeaver Enterprise Portal. SAP published the fix on November 11, 2025 as SAP Note 3660969; the KEV addition moves it from “patch when convenient” to “active exploitation signal, prioritize now.”
Quick summary
| Field | Value |
|---|---|
| CVE | CVE-2025-42884 |
| Product | SAP NetWeaver Enterprise Portal |
| Affected components | EP-BASIS 7.50, EP-RUNTIME 7.50 |
| Weakness | CWE-943 — Improper Neutralization of Special Elements in Data Query Logic (JNDI injection) |
| CVSS v3.1 | 6.5 (Medium), AV:N/AC:L/PR:N/UI:N/S:U/C:L/I:L/A:N — SAP CNA |
| NVD status | Analyzed |
| KEV added | 2026-11-20, due 2026-11-23, ransomware: Unknown |
| Fix | SAP Security Note 3660969 |
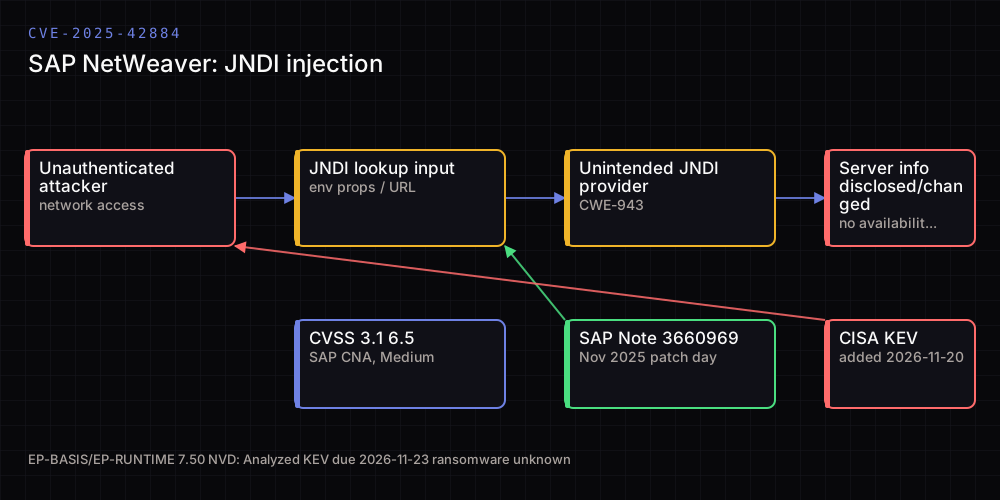
Technical view
Per NVD and CVE records, an unauthenticated attacker can inject JNDI environment properties or pass a URL used during JNDI lookup operations. The application may then access an unintended JNDI provider, leading to disclosure or modification of server information. No availability impact is reported.
That distinction matters: the official records state C:L, I:L, A:N. Some secondary writeups reflexively turn any JNDI injection into RCE; primary NVD/CISA/SAP records do not say that for this CVE. Assess impact against the official vector.
Why it entered KEV
CISA adds CVEs to KEV based on evidence of active exploitation. For CVE-2025-42884, the KEV entry shows active exploitation status; knownRansomwareCampaignUse is Unknown. Unknown ransomware use is not “no exploitation.”
The BOD 26-04 due date for U.S. federal civilian agencies is November 23, 2026. Not binding for private sector, but a strong prioritization signal.
Scope and uncertainties
- Affected versions: CISA/NVD list EP-BASIS 7.50 and EP-RUNTIME 7.50. SAP Note 3660969 details may require portal access; confirm your exact SP/package against the note before patching.
- Attack precondition: Network access appears sufficient (
PR:N,UI:N), but exposure depends on whether the portal component is reachable. - RCE claim: Not verified in primary sources. Do not claim it.
What to do
- Apply SAP Note 3660969. Inventory affected EP-BASIS/EP-RUNTIME 7.50 systems and patch per the note.
- Reduce portal exposure. Do not expose NetWeaver Enterprise Portal directly to the internet; place behind WAF/VPN/access controls where possible.
- Review JNDI/LDAP egress. Check logs and egress controls for unexpected outbound JNDI/LDAP/RMI connections.
- Treat the KEV date seriously. Even outside federal scope, the 2026-11-23 due date is a useful urgency marker.
What not to claim
- Do not call it confirmed RCE; primary records report C:L/I:L/A:N.
- Do not claim ransomware use; CISA reports
Unknown. - Do not say there is no patch; SAP note was published November 11, 2025.
- Do not deprioritize only because CVSS is 6.5; KEV addition is an exploitation signal.
Status
As of November 21, 2026, this is a flaw with completed NVD analysis, a SAP fix from 2025, and a CISA KEV addition. The 6.5 CVSS and CWE-943 are SAP-sourced; CISA SSVC says exploitation: active, while KEV marks forensicTriage: No and ransomware use as Unknown. The impact vector is C:L/I:L/A:N, and primary records do not claim RCE. The unresolved piece is the exact SP/package matrix covered by SAP Note 3660969; match your own release against the note.